

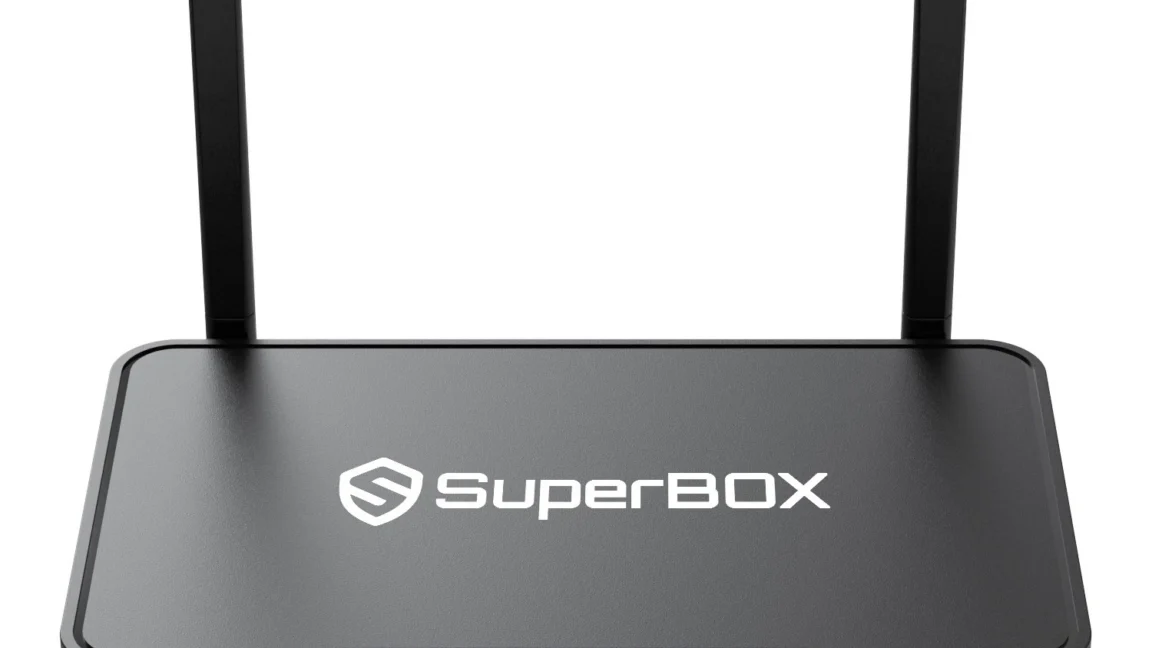
Security firm Plume released research detailing how residential proxy networks integrated into digital media streaming devices pose significant cybersecurity risks to home users. These devices, which offer free access to movies and television shows in exchange for using a portion of the user’s internet bandwidth, funnel millions of home connections into unified networks that attackers can utilize to route malicious traffic while evading detection by legitimate online services.
The analysis focused on SuperBox, an Android-based media player offering pirated content, though Plume noted that dozens of similar streaming devices contain the same vulnerabilities. The devices are configured with most Android security protections disabled by default, allowing pre-installed and third-party applications to run with root-level administrative access. This configuration exposes the Android Debug Bridge (ADB) to the internet and grants root access without authentication, enabling remote attackers to install malware silently and bypass all standard Android security measures including signature verification and permission dialogs.
Much of the danger derives from how the proxy functionality operates within the devices. Applications that provide proxy services maintain persistent outbound encrypted connections to proxy servers, which home routers cannot block. Additionally, the ADB port remains exposed to internet-connected attackers despite users believing their devices are protected behind their home routers. Researchers demonstrated that attackers can leverage this combination to install malicious applications that compete for system resources and damage the reputation of the IP address being used.
The research included a controlled experiment on the Popanet residential proxy network. Over a three-week period, researchers operating a honeypot node recorded 1,352 distinct attempts to access the ADB port, confirming that theoretical vulnerabilities were being actively exploited. Even proxy services implementing protections against accessing local networks can be circumvented using special wildcard addresses that route traffic through the device’s local IP.
Plume researchers warned that compromised devices often become infected with multiple malware families, with device owners remaining unaware of the additional botnet activity consuming their bandwidth and degrading their network reputation. The attackers conducting these secondary infections are frequently paying customers of the primary proxy service itself.
Article Attribution | Read More at Article Source
Article summary produced by Claude AI